Developer settings and files
API keys with explicit scopes, outbound events, and how uploaded files are handled.
On this page
Where this comes from
This guide is distilled from docs/SAAS-REGISTRIES.md and src/features/storage. When the guide and Growth-OS disagree, that document is the one to trust, and the difference is worth reporting.
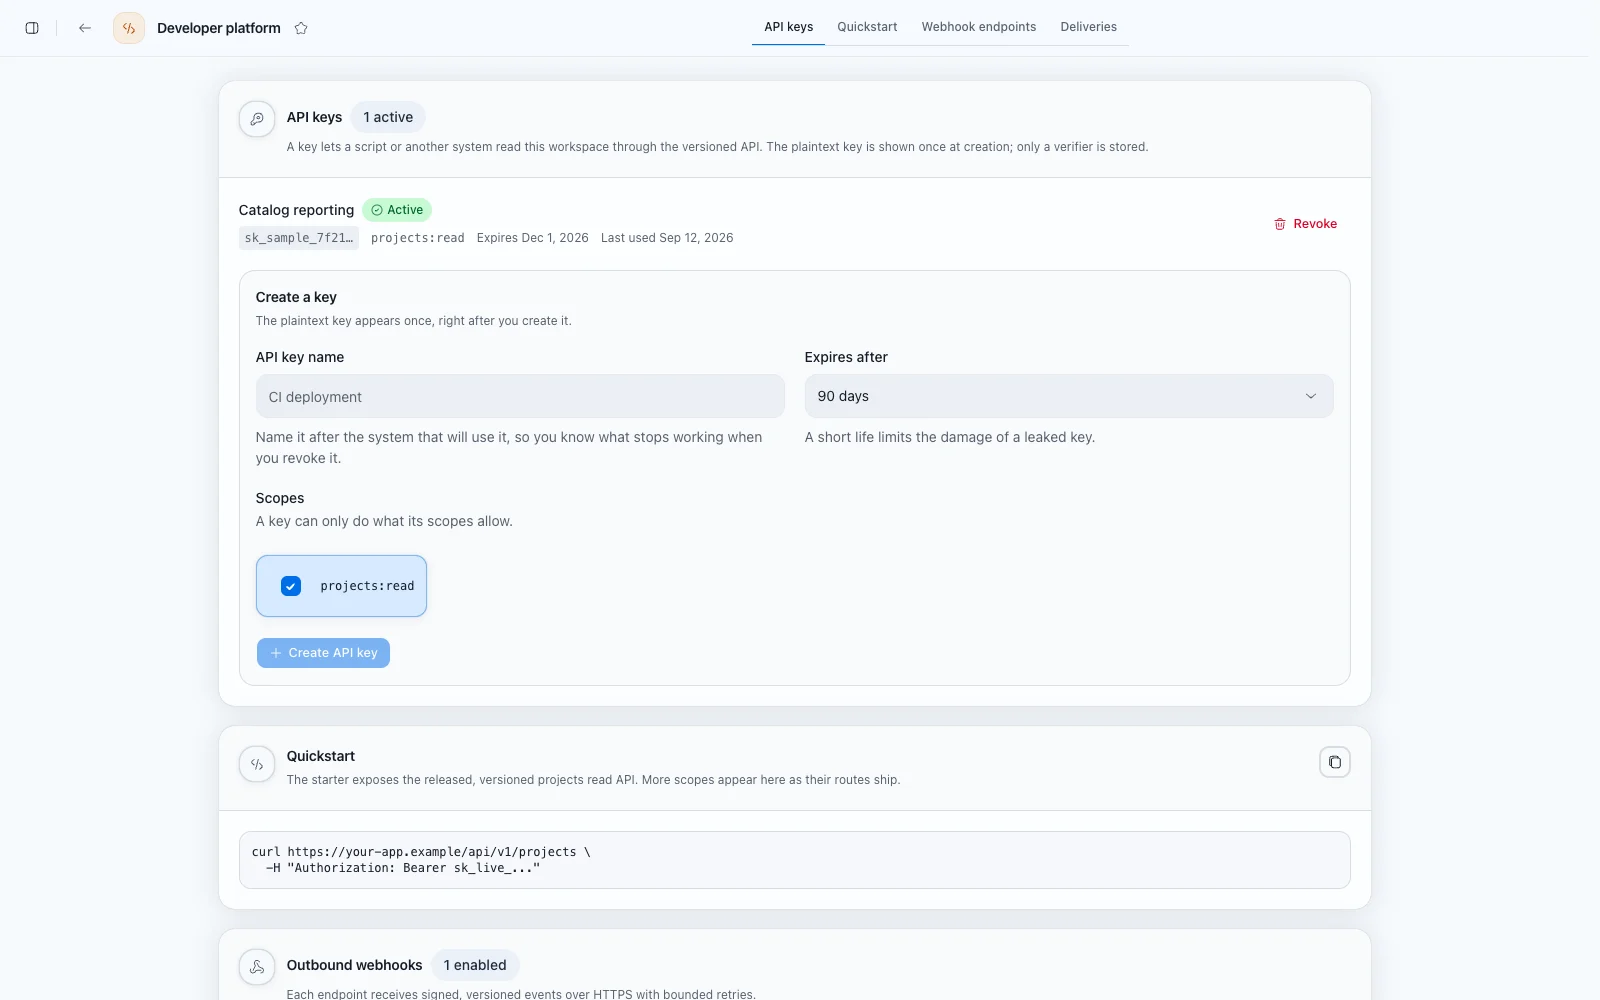
Keys carry scopes
API keys are managed by administrators and carry explicit scopes. Versioned endpoints check tenant access and usage again on every call, so a key never reaches data its scope does not name.
Outbound events are signed, use strict schemas, retry a bounded number of times, keep their attempt history, and can be replayed by someone authorized to do it.
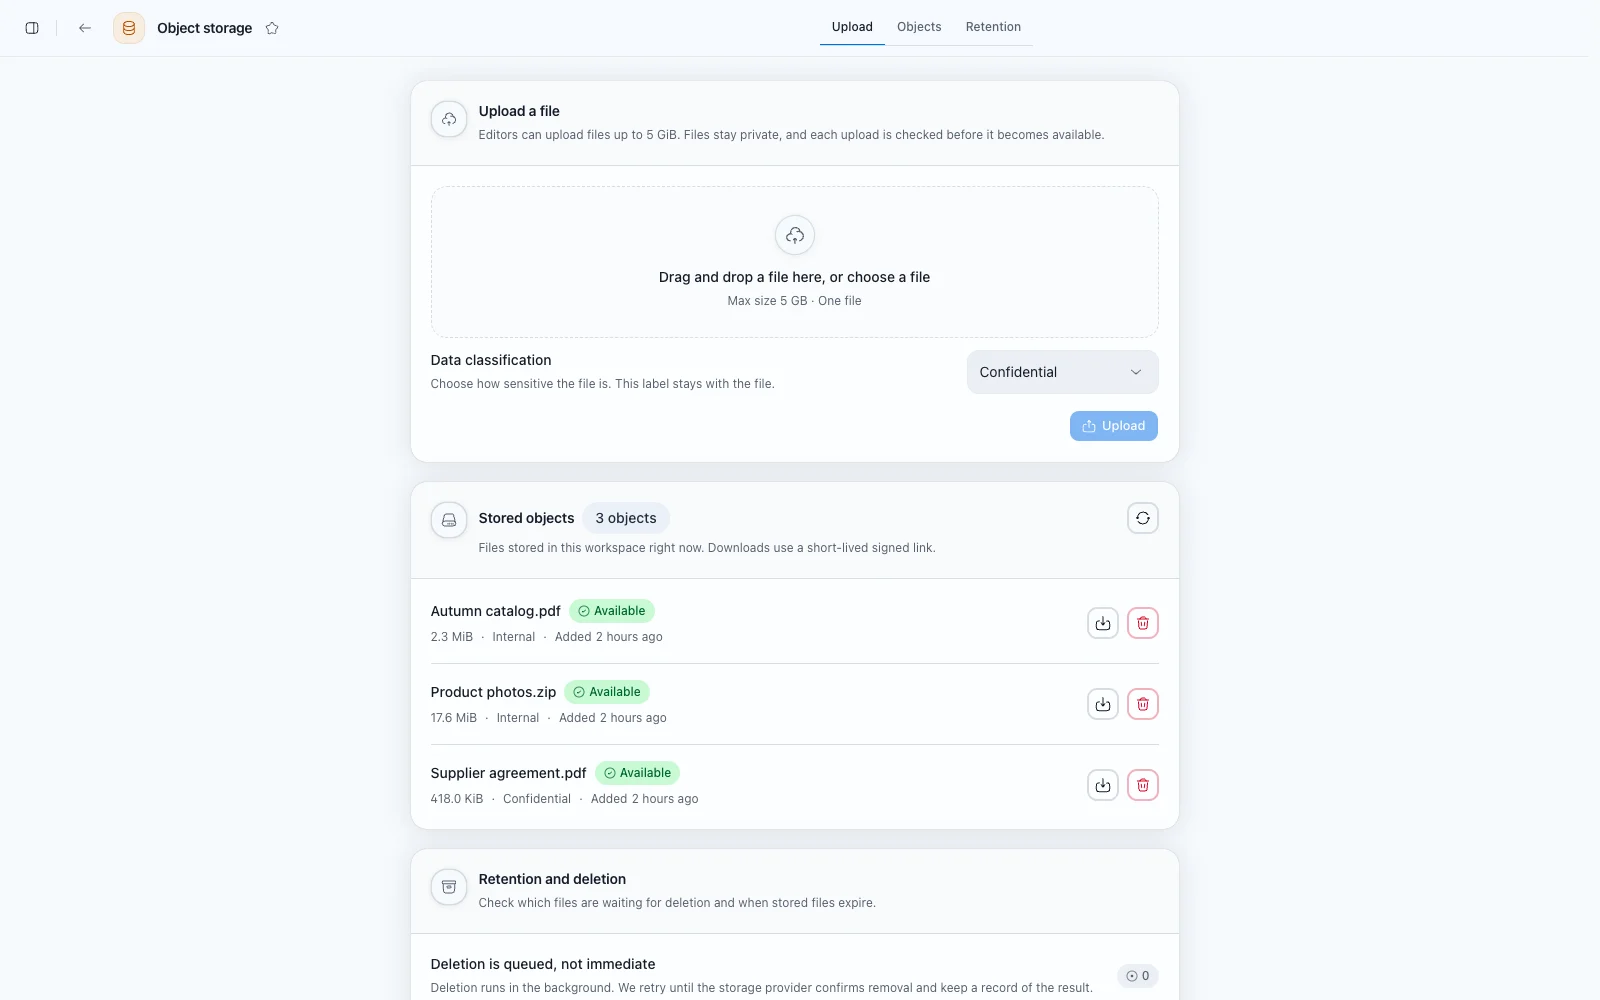
Files stay private
Uploads are validated by checksum, stored privately, and downloaded through signed access. Deleting a file removes it logically first and the physical cleanup is visible and retried, so a failed cleanup is a state you can see rather than a silent leak.
Playbook screenshots follow the same path: they are compressed in your browser before they are sent, stored with the playbook in this project, never shared outside it, and removed with the record.
Was this page helpful?
Feedback is stored only in this browser.